Individual Informed Consent - HIPAA requires healthcare companies to obtain informed consent before collecting PHI. This includes clear direction on how patient data will be collected, used, and protected. Obtaining consent also ensures transparency and trust.
Healthcare
HIPAA Compliance and Customer Data
Protecting Patient Privacy While Providing Optimal Patient Care and Experiences
What is HIPAA Compliance?
HIPAA is a US federal law enacted in 1996 to establish national standards for protecting individuals' sensitive health information. While initially focused on healthcare providers and insurance companies, the law's scope has expanded to cover a wide range of entities that handle Protected Health Information (PHI).
HIPAA compliance ensures organizations and businesses handle PHI securely, maintain the privacy of individuals' health information, and establish proper data collection and management practices. It not only applies to healthcare providers, health plans, and healthcare clearinghouses (collectively called Covered Entities), but also to their partners or any entity that manages or handles or processes PHI (collectively called Business Associates).
HIPAA compliance ensures organizations and businesses handle PHI securely, maintain the privacy of individuals' health information, and establish proper data collection and management practices. It not only applies to healthcare providers, health plans, and healthcare clearinghouses (collectively called Covered Entities), but also to their partners or any entity that manages or handles or processes PHI (collectively called Business Associates).
Compliance with the Health Insurance Portability and Accountability Act (HIPAA) is not only essential for healthcare providers and insurers but also for any entity that handles patient data, especially sensitive health information. By prioritizing HIPAA compliance, healthcare providers can protect patient privacy, mitigate data breach risks, and avoid legal consequences. Adhering to HIPAA regulations also ensures ethical data collection, secure data transmission, access controls, and proper data retention practices while providing optimal patient care and experiences – which can be supported by a Customer Data Platform (CDP).
Why HIPAA Compliance Matters to Healthcare Organizations
Protecting Customer Privacy
Mitigating Data Breach Risks
Avoiding Legal Exposure
HIPAA compliance plays a vital role in protecting patient privacy and confidentiality. By adhering to the law’s standards, businesses demonstrate their commitment to maintaining the privacy and security of patient data, fostering trust and confidence.

Compliance with HIPAA regulations helps businesses implement robust security measures to prevent data breaches. Reducing the risk of unauthorized access to patient data, organizations can also avoid negative financial or brand impacts.

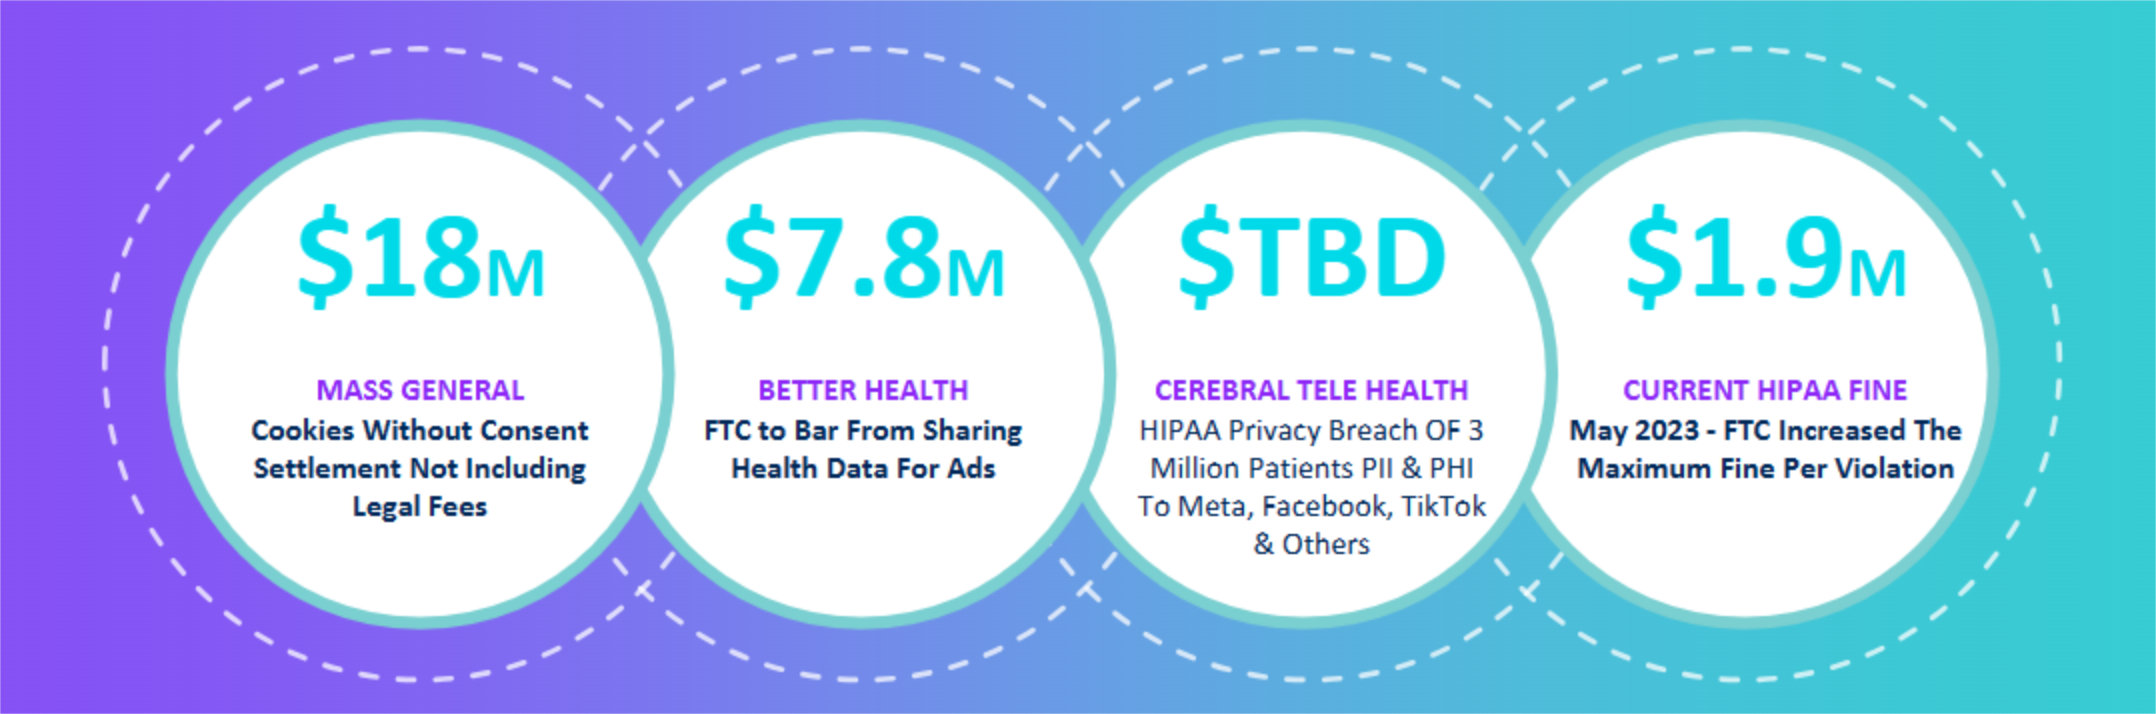
HIPAA non-compliance can lead to severe legal consequences, including hefty fines and legal liabilities. Ensuring compliance protects businesses but also safeguards patient rights, as HIPAA grants individuals the right to take legal action for privacy violations.

HIPAA Compliance and Data Collection
Data collection is an integral part of any business operation, and it's essential for healthcare organizations to handle patient data with the utmost care, especially when it comes to PHI. Here's how HIPAA compliance impacts data collection:
1
2
Secure Data Transmission - HIPAA mandates secure data transmission when PHI is shared electronically. Encryption protocols, such as Secure Sockets Layer (SSL) or Transport Layer Security (TLS), should be utilized to protect data during transmission, reducing the risk of breaches.
3
Access Controls and Audit Trails - Healthcare companies must implement access controls to ensure only authorized personnel can access PHI. Maintaining audit trails also helps track who accessed the data and when, providing a transparent record of data usage reducing risks of data misuse.
4
Data Retention and Disposal - HIPAA requires organizations to establish retention policies for PHI and ensure secure disposal when data is no longer needed. Proper data retention and disposal practices prevent data from being retained indefinitely avoiding unauthorized access.
The Role of Customer Data Platforms (CDPs) in HIPAA Compliance
CDPs can play a significant role in helping organizations achieve HIPAA compliance while they focus on creating personalized experiences for their customers, as CDPs are powerful solutions that unify customer data from various sources, which results in an accurate, trusted information profile of the patient. Specifically with respect to HIPAA compliance, CDP designs will ensure that healthcare organizations can successfully address the following areas of focus:
Data Security and Encryption
Access Controls and Permissions
Auditing and Monitoring
Consent Management
Data Retention and Deletion
Vendor Management and Compliance
CDPs are connected to robust data collection technologies that are designed to provide secure handling of all PHI that surfaces on the devices patients are using. Encryption and hashing of this data takes place immediately upon these devices, which is critical for HIPAA compliance as it assures the healthcare organization that they become stewards of this data in an appropriate format. Encryption ensures that sensitive information remains secure from the moment it surfaces to the moment that the Healthcare organization takes ownership of it and places it at rest. By implementing encryption protocols within the CDP infrastructure, organizations can comply with HIPAA requirements for safeguarding PHI.
HIPAA requires organizations to implement strict controls to limit access to PHI, and this applies to both internal personnel as well as Business Associates. CDPs can enforce role-based access controls, ensuring that only authorized personnel can access and handle sensitive patient data, or any subset of it that is relevant for the purpose. This reduces the risk of unauthorized data exposure.
CDPs often offer auditing and monitoring capabilities that enable organizations to track data access and changes. These features help maintain an audit trail of who accessed PHI, what changes were made, and when. In addition, CDP profiles will change over time, based on activity or events that take place with the patient journey – these changes can be automated to improve operational efficiency, and the impact of this automation upon the profile is also audited, giving the healthcare organization a complete data lineage and timeline to ensure compliance. By monitoring data activity within the CDP, organizations can identify and respond to any suspicious or unauthorized access, ensuring compliance with HIPAA’s security requirements.
HIPAA requires obtaining patient informed consent before collecting and using their PHI. CDPs can facilitate consent management by providing tools that produce digital consent forms, capture the associated privacy preferences chosen, and enforce the implied data flows that they correspond to. This allows organizations to ensure data collection and processing activities align with the specific consents given by patients, enhancing compliance with HIPAA’s consent requirements.
HIPAA also mandates proper data retention and disposal practices. CDPs can assist organizations in managing data retention periods and automating data deletion when it is no longer needed. By implementing data lifecycle management within the CDP, organizations can ensure that PHI is retained and disposed of in accordance with HIPAA guidelines.
If an organization uses a CDP provided by a third party vendor, it’s crucial to ensure that the vendor itself is HIPAA compliant. Organizations should carefully evaluate the vendor’s security measures, data handling practices, and compliance certifications. Working with a HIPAA-compliant CDP vendor helps maintain compliance throughout the data management process because the built-in integrations to Business Associate technology are fully secured and automated to eliminate errors and ensure consistency.
It's important to note that while CDPs can provide valuable tools and features to support HIPAA compliance, organizations must still implement appropriate policies and procedures to ensure overall compliance. Regardless, CDPs should be considered a part of the overall compliance strategy, addressing other aspects of HIPAA requirements, such as administrative, physical, and technical safeguards.
HIPAA Compliance and Tealium
Tealium empowers healthcare organizations to harness the power of their patient data to create optimal patient experiences and outcomes while maintaining compliance with regulations and privacy laws. Healthcare organizations can use the Tealium services to facilitate their HIPAA compliance efforts, while creating a single view of the customer as the foundation to create personalized patient experiences.
Imagine creating better segmentation, developing richer experiences using new data sources, automating data operations, and ensuring privacy is upheld, without all the regulatory risk – you can with Tealium.
Imagine creating better segmentation, developing richer experiences using new data sources, automating data operations, and ensuring privacy is upheld, without all the regulatory risk – you can with Tealium.
Why Tealium
In addition to the benefits of using a CDP as stated above, Tealium has undergone independent third party audits to validate the Private Cloud offering is compliant with the security and privacy requirements under HIPAA. Because of this attestation of compliance, Tealium can and does enter into Business Associate Agreements (BAA) with its customers. Tealium also enters into BAAs with all Tealium subprocessors who process PHI on Tealium’s behalf.
Best in Class Architecture for HIPAA Compliant Data Collection & Reporting
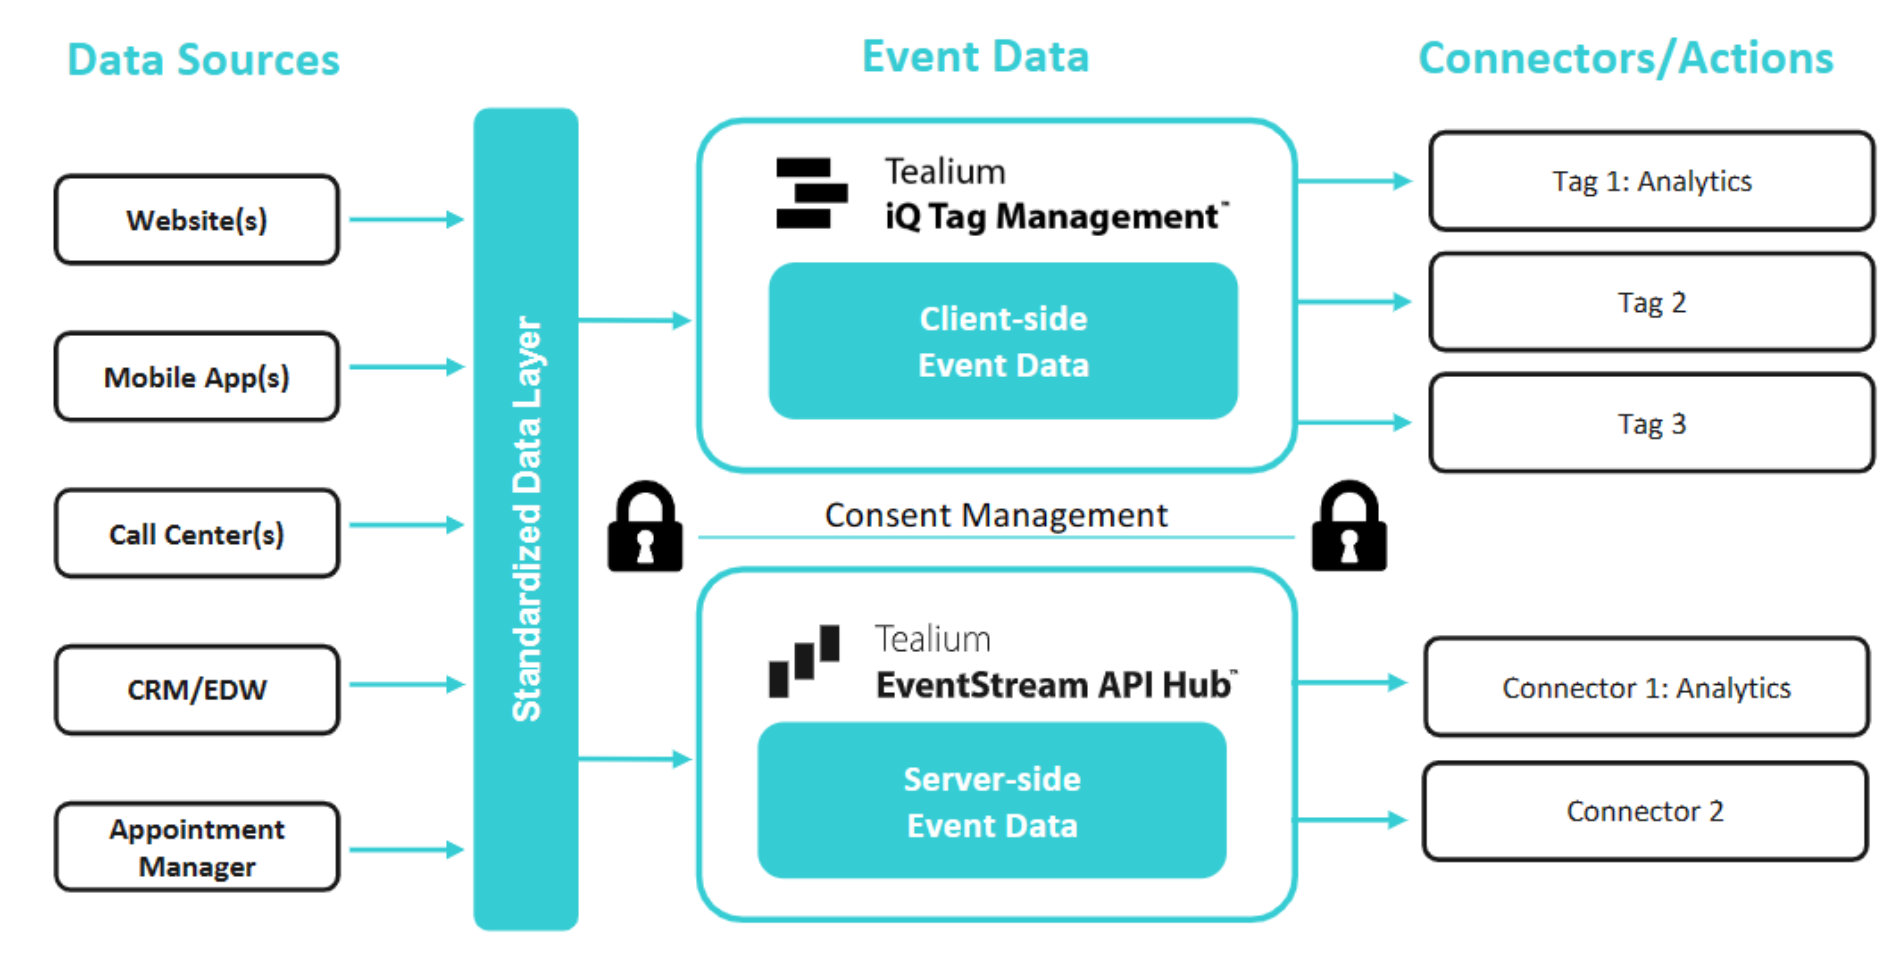
How Tealium Stacks Up Against Other Vendors
Tealium has a proven track record with leading healthcare and pharma companies and is a solution that is flexible as it integrates with existing technology as well as supports privacy and real-time data.

Collect Privacy-Conscious
Customer Data
It’s your customer, so collect your own customer data instead of relying on third party vendors.
Organizations who establish a privacy-centric data foundation can obtain, maintain, and respect consent throughout the customer lifecycle and as a result, build customer trust.
Organizations who establish a privacy-centric data foundation can obtain, maintain, and respect consent throughout the customer lifecycle and as a result, build customer trust.

Know and Honor
Customer Preferences
Customers need a way to express their choice, and businesses must recognize
and honor their preferences.
Tealium’s identity resolution and consent management capabilities give enterprises confidence to uphold privacy choices across their customer
experience efforts.
and honor their preferences.
Tealium’s identity resolution and consent management capabilities give enterprises confidence to uphold privacy choices across their customer
experience efforts.

Add Visibility, Control and
Efficiency with Sensitive Data
Sensitive customer data requires strict handling, collection, and monitoring (to
avoid mistakes!).
Tealium provides tools to control your data practices from the point of collection throughout the data lifespan in order to reduce any long term risk to your business.
avoid mistakes!).
Tealium provides tools to control your data practices from the point of collection throughout the data lifespan in order to reduce any long term risk to your business.

Flexible, Independent
Tealium works with healthcare organizations to integrate across very niche legacy tools and data formats, no matter what they are. Web, mobile, CX, wearables, devices, etc. We’ll
help integrate however you want, using the data schema you want, to give you ultimate flexibility at a reasonable cost.
We won’t try to cross-sell you to a cloud or make you fit our schema.
help integrate however you want, using the data schema you want, to give you ultimate flexibility at a reasonable cost.
We won’t try to cross-sell you to a cloud or make you fit our schema.

Trusted Tech
Tealium enables you to break down data silos, resolve identity, build persistent customer profiles and define audiences all within a HIPAA-compliant private cloud (2 options). We have many examples in production. Unify and act on patient data in real-time. We will sign a BAA (and have signed many).

Privacy Orchestration
Tealium provides the infrastructure to orchestrate privacy preferences through the journey. With our integrated infrastructure, gives extra control over data flow. Enforce preferences and better honor privacy from a central hub. Send deletion requests and other changes in real-time. Manage organizational compliance and privacy goals centrally.